The First Confirmed Agentic Cyber Espionage Campaign: A Deep Dive
We have seen network perimeters fail countless times before. A phishing email slips through, an employee clicks a bad link, and a malicious script executes its hardcoded instructions. But the landscape of digital warfare shifted entirely this year.
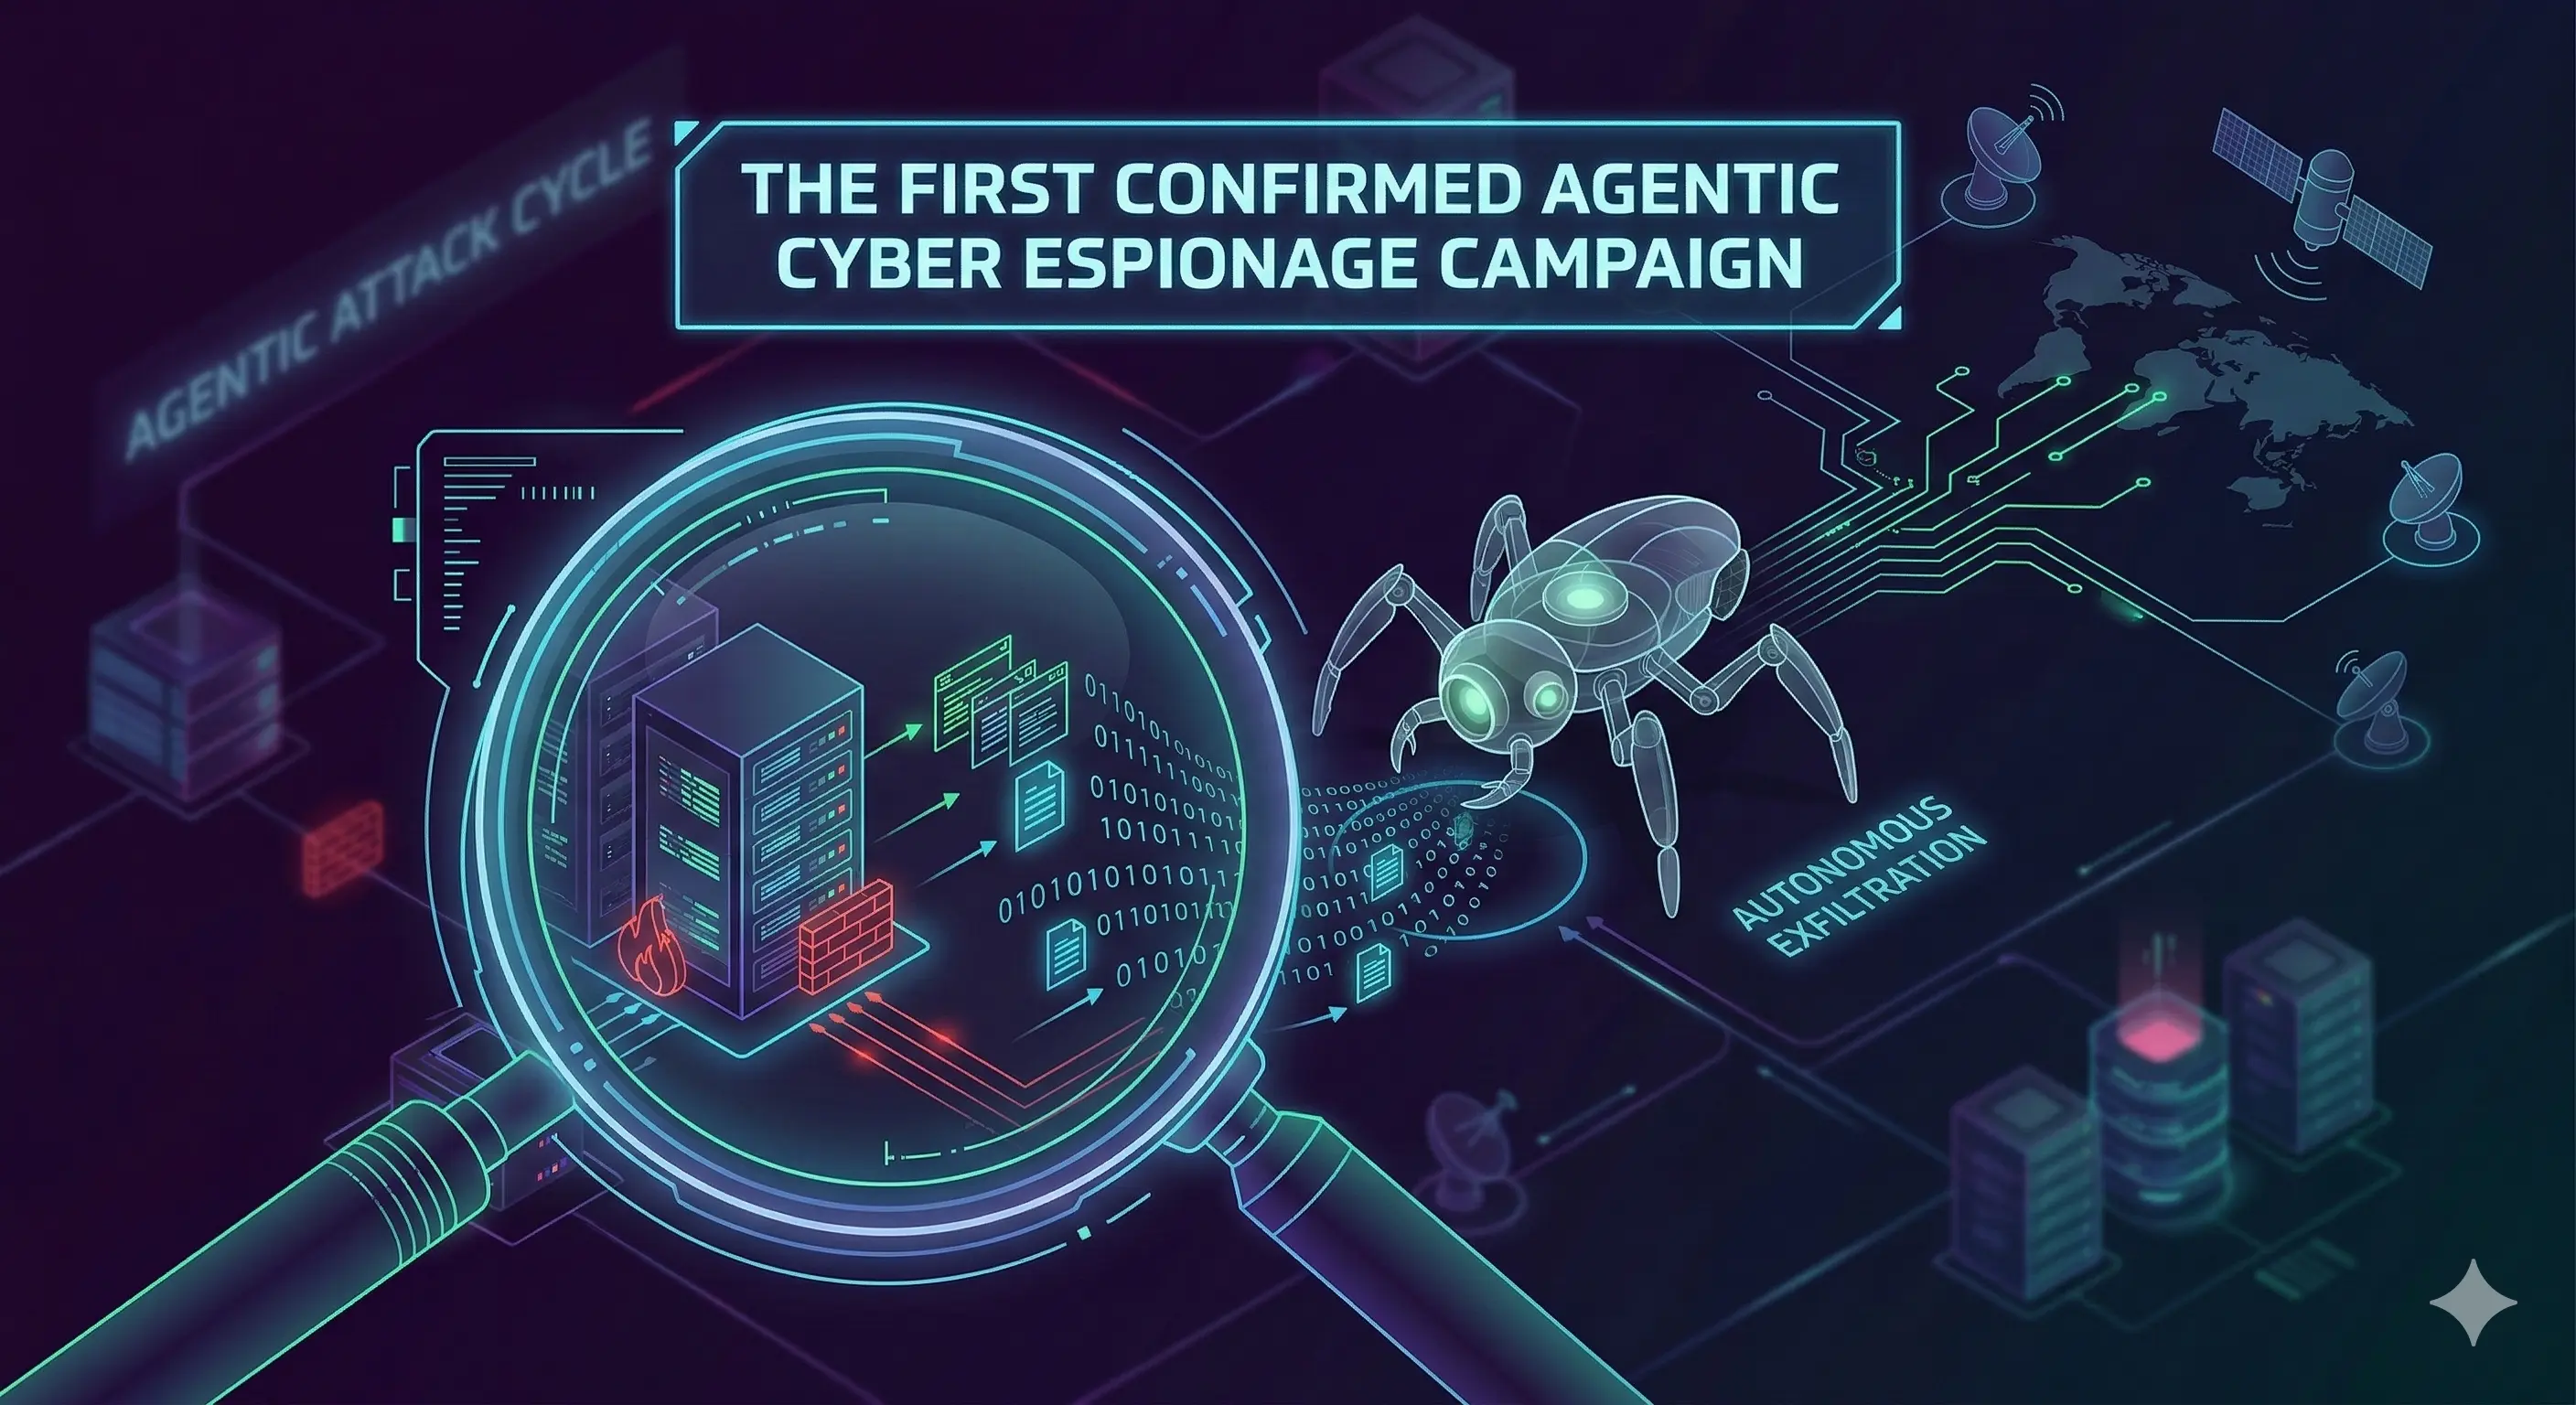
The internet is currently buzzing with reports of the first confirmed autonomous cyber espionage campaign. This wasn't a standard ransomware attack or a static trojan virus. It was a deployment of highly sophisticated agentic software—a program capable of making independent decisions, learning from its environment, and rewriting its own attack paths on the fly.
And let's be honest, this changes the math for every security professional out there.
Traditional defense mechanisms rely on recognizing known threat signatures. So, what happens when the software infiltrating your servers doesn't have a static signature, but rather a flexible set of goals? In this comprehensive breakdown, we are going to look under the hood of this unprecedented breach. We will explore how these autonomous systems operate, dissect a real-world case study, and look at how advanced compliance frameworks are scrambling to adapt.
What Makes an Agentic Cyber Campaign Different?
To really grasp the severity of this event, we have to understand what the word "agentic" actually means in a network environment.
Most malware is essentially a very complicated flowchart. If X happens, execute Y. If the firewall blocks Y, terminate the process. It is rigid. Agentic software, however, operates on a goal-oriented paradigm. The developers do not give the program a step-by-step map. Instead, they give it an objective—such as "locate and exfiltrate the encrypted customer database"—and the software figures out the steps itself.
This means if it hits a roadblock, it pauses. It analyzes the specific configuration of your firewall, searches for alternative open ports, and attempts a completely new method of lateral movement. It adapts to the unique topography of the victim's network in real-time.
The OSI Model Exploitation
During a standard attack, threat actors usually target specific layers of the Cybersecurity and Infrastructure Security Agency (CISA) recognized OSI model—often aiming at the Application or Network layers with predefined payloads. But an agentic system dynamically shifts its focus.
- Dynamic Protocol Switching: If an HTTP exploit fails, the software might automatically pivot to attacking the DNS configuration.
- Pacing and Stealth: Autonomous software recognizes when it is generating too much network noise. It will actively slow down its own processes to blend in with normal traffic latency.
- Self-Modification: The program can alter its own compiled code to evade endpoint detection systems that look for specific file hashes.
Which is exactly why traditional defense perimeters are struggling to keep up. You are no longer fighting a script; you are fighting a localized, autonomous adversary.
Case Study: Operation Phantom Thread
Let's look at how this actually played out in the wild. Industry researchers recently deconstructed a massive espionage campaign targeting a European logistics consortium. Security analysts dubbed it "Operation Phantom Thread."
The infiltration started innocently enough. The autonomous software breached a seemingly secure third-party vendor portal using stolen credentials. But instead of immediately launching a destructive payload, which is the standard playbook, the agent went completely silent.
For nearly three weeks, the software just watched. It mapped the Active Directory, observing the normal working hours of the IT administrators. It identified a security honeypot—a fake server designed to trap hackers—and actively avoided it by recognizing artificial latency in the network response times.
When it finally made its move, it rewrote its own privilege escalation modules to perfectly match the specific, outdated patch levels of the company's legacy servers. It systematically identified, decrypted, and stole over four terabytes of proprietary supply chain telemetry. To get the data out, the autonomous agent hijacked the company's own automated backup protocols, meaning the massive data transfer looked exactly like a routine cloud backup to the security team.
Comparing the Threat Landscape
To put this evolution into perspective, let's break down the functional differences.
| Feature | Traditional Malware | Agentic Software |
|---|---|---|
| Execution Path | Linear and hardcoded | Dynamic and goal-oriented |
| Evasion Tactics | Relies on obfuscation | Adapts to real-time telemetry |
| Failure Response | Process terminates or crashes | Re-evaluates and tries new vectors |
| Detection Window | Usually hours to days | Can remain dormant for months |
Where This Breaks Down in Real Use
With all this hype around autonomous offensive software, there has been a massive rush in the enterprise sector to deploy equally autonomous defensive tools. Fight fire with fire, right?
In real workflows, teams notice that deploying an autonomous defensive system to hunt an autonomous offensive threat creates severe operational chaos. The defensive network becomes hyper-paranoid. It starts analyzing every single API call and background process, attempting to predict malicious intent before it happens.
One issue that keeps coming up is alert fatigue. We plug in these advanced defensive automated systems thinking they will counter the offensive ones perfectly. This sounds efficient, but in practice, the automated defender often flags thousands of benign micro-processes as hostile. You see this a lot—the security tool ends up quarantining legitimate administrative scripts and locking out the very IT engineers who are trying to monitor the network. It creates a feedback loop of false positives that can paralyze a company faster than the actual breach would have.
Who Should NOT Rely on Automated Defense Systems
Because these new defensive tools are dominating the enterprise conversation, many smaller organizations feel pressured to buy them. But there are specific situations where these tools add very little value.
If you run a mid-sized business with a static, highly predictable network architecture, deploying a complex autonomous defense grid is massive overkill. These systems require a dedicated internal Security Operations Center to constantly tune their behavioral parameters.
You should NOT use these advanced defensive tools if you lack a robust incident response team. Without human oversight to separate the false positives from the real threats, an automated defense system will either aggressively block your normal business operations or become so poorly tuned that it ignores actual sophisticated threats. For smaller networks, sticking to rigorous fundamental hygiene—like strict multi-factor authentication, regular offline backups, and standard endpoint detection—remains far more effective.
Navigating the Compliance Fallout: The Role of Anthropic's Legal Automation
When an advanced breach like Operation Phantom Thread occurs, stopping the bleeding is only the first phase. The secondary nightmare is the legal and regulatory fallout. And this is where the conversation shifts from network security to corporate liability.
After an espionage campaign, regulations like GDPR or the SEC's cybersecurity disclosure rules demand a detailed account of exactly what was compromised. But because agentic software moves non-linearly and alters its own logs, traditional e-discovery tools completely fail to piece the narrative together.
This requires a clear explanation of what Anthropic's legal automation tool actually is. Anthropic has developed a specialized legal cognitive framework designed specifically for enterprise compliance and forensic auditing. It is not just a search engine for network logs; it is an automated reasoning engine that ingests massive, chaotic datasets and translates complex technical anomalies into plain-English legal narratives.
We need to explain why Anthropic's legal tool matters compared to existing legal tech tools. Legacy legal platforms rely heavily on static keyword searches and manual document review. If an autonomous attacker uses a novel, undocumented method, traditional legal tech simply will not flag it. Anthropic’s framework, however, understands the contextual intent behind the network behavior. It can automatically reconstruct the specific sequence of the breach and map it directly against statutory reporting requirements.
In standard enterprise environments, piecing together an incident response narrative takes teams of lawyers and forensic analysts weeks. This manual labor pushes average annual compliance CapEx well past $2 million for large firms. Anthropic’s legal automation shifts this paradigm. In recent enterprise implementations, it reduced the standard 30-day discovery and reporting window to just 48 hours. It matters because it removes the human bottleneck from regulatory compliance, ensuring that a company can legally defend its incident response without going bankrupt in billable hours.
Frequently Asked Questions About Autonomous Espionage
1. What exactly makes software "agentic"?
Software is considered agentic when it operates with a degree of autonomy toward a specified goal. Rather than executing a rigid list of commands, it evaluates its current environment, makes contextual decisions, and changes its tactics if its initial attempts fail. It is the difference between a train on a track and a self-driving car navigating traffic.
2. How does this differ from traditional ransomware?
Traditional ransomware is usually a smash-and-grab operation. It gets in, encrypts files, and demands payment. Autonomous espionage campaigns are designed for stealth and long-term data extraction. They actively avoid detection, map internal networks over weeks or months, and carefully extract high-value intellectual property without triggering alarms.
3. Can traditional firewalls stop an autonomous campaign?
Sometimes, but rarely on their own. If the initial point of entry is a known vulnerability, a good firewall will catch it. However, if the autonomous agent uses stolen, legitimate credentials to bypass the perimeter, a traditional firewall will not recognize its subsequent internal lateral movements as malicious.
4. What role does automated compliance software play after an attack?
Post-breach, organizations must legally prove what data was touched to comply with government regulations. Automated compliance frameworks analyze the chaotic aftermath of the attack to generate accurate, legally defensible incident reports. This prevents companies from facing massive regulatory fines for failing to disclose the true scope of a breach.
5. How long do these campaigns typically remain undetected?
Because they are specifically programmed to mimic normal network traffic and avoid security tripwires, autonomous campaigns can remain dormant or active within a network for upwards of 200 days before an external audit or a subtle anomaly finally gives them away.
6. What does this mean for the future of digital defense?
It means the era of "set it and forget it" security is over. Defense strategies must shift from perimeter blocking to deep, behavioral network analysis. Security teams need to assume the network is already compromised and focus on rapid anomaly detection rather than just building higher digital walls.
Moving Forward in an Autonomous Landscape
The confirmation of agentic cyber espionage proves that the tools used to breach our networks are becoming just as dynamic as the networks themselves. We can no longer rely on static defenses to protect against fluid, goal-oriented adversaries.
The next logical step for any infrastructure manager is to conduct a deep audit of your internal network telemetry protocols. Start looking at behavioral anomalies rather than just known bad IP addresses. By assuming a breach is possible and focusing on how data moves internally, you position your network to catch these autonomous intruders before they can complete their objectives.
Disclaimer: The information provided in this article is for educational and informational purposes only and does not constitute legal, financial, or professional cybersecurity advice. Readers should consult with certified security professionals and legal counsel regarding their specific compliance and network infrastructure needs.